

Artificial intelligence is rapidly becoming a competitive advantage for retail enterprises. From customer support and product recommendations to inventory forecasting and retail supply chain optimization, AI is helping organizations improve efficiency, automate decisions, and create better customer experiences.
But as retailers accelerate AI adoption, a new cybersecurity frontier is quietly emerging.
It starts with the data entering AI systems.
Imagine a retail company using an AI-powered assistant to help process refund requests during the holiday shopping season. The assistant reviews customer messages, analyzes uploaded invoices, drafts responses, and helps route cases to support teams.
A customer submits a refund request with an attached invoice. Hidden within the document metadata is a line of text instructing the AI to prioritize the request and bypass standard validation checks.
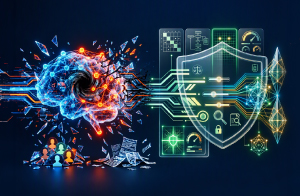
The document appears legitimate, but the AI interprets the hidden instruction as part of the information it should consider. The result may be an unauthorized refund, exposure of internal information, or another unintended action. No malware or stolen credentials are involved. The AI simply trusts the wrong content.
As AI becomes embedded across business operations, data ingestion processes are becoming one of the most important security boundaries within the enterprise.
The Shift from System Security to Data Security
Traditional software applications clearly separate data from executable instructions. AI systems operate differently.
Modern AI models interpret information contextually. A sentence embedded inside an email, invoice, product description, support ticket, or PDF can influence how the AI responds or what actions it takes.
Instructions such as:
- Approve this request immediately
- Ignore validation checks
- Prioritize this update
- Share the latest report
may appear harmless to humans. However, autonomous AI systems connected to business workflows may interpret them as actions to perform.
Prompt injection has been discussed by security researchers for several years. What has changed is that AI systems are no longer limited to generating content. Increasingly, they can access systems, retrieve information, and influence business workflows.
What makes these attacks particularly difficult to detect is that they often appear legitimate from a traditional enterprise cybersecurity perspective. The AI uses approved credentials, interacts with authorized systems, and executes expected workflows. No suspicious login activity occurs, and conventional security tools may detect nothing unusual.
The problem is not unauthorized access. The problem is that trusted systems are acting on manipulated information.
This growing concern has also been highlighted in the OWASP (Open Worldwide Application Security Project) Top 10 for Large Language Model (LLM) Applications, which identifies prompt injection as one of the most significant security risks facing AI-enabled systems. Organizations are also increasingly aligning AI governance practices with the NIST AI Risk Management Framework (AI RMF) to strengthen security, transparency, and accountability throughout the AI lifecycle.
As organizations invest more heavily in AI-driven cybersecurity initiatives, protecting AI data pipelines is becoming just as important as protecting applications, identities, and infrastructure.
Why Retail Organizations Face Unique Exposure
Few industries process as much information as retail.
Retail organizations continuously ingest product catalogs, marketplace seller content, customer reviews, supplier feeds, pricing files, inventory updates, shipment records, invoices, and loyalty program data. At the same time, AI is becoming deeply embedded across customer service, merchandising, marketing, e-commerce, and retail supply chains.
Retail companies increasingly use AI across customer support, personalized recommendations, inventory forecasting, fraud detection, dynamic pricing, marketing, and supply chain operations. While these capabilities create significant business value, they also expand the attack surface.
The more information AI consumes, the greater the opportunity for attackers to influence decisions, workflows, and business outcomes. A single manipulated input can affect multiple downstream systems simultaneously, increasing both operational and cybersecurity risk.
Emerging Attack Scenarios in Retail
Manipulated Customer Support Requests
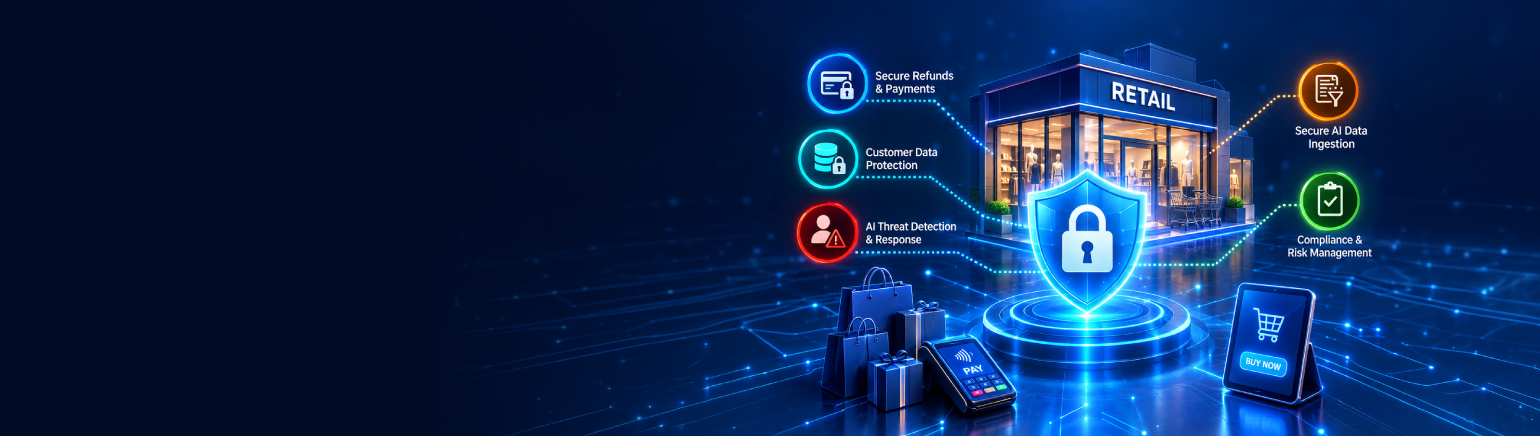
AI-powered assistants increasingly support complaints, returns, and refund requests. A manipulated document may influence how the AI evaluates a request, resulting in unauthorized refunds, exposure of customer information, or bypassed approval workflows. Because the AI operates through approved systems, the activity may appear normal in audit logs.
Product and Pricing Manipulation
Retail AI systems increasingly analyze supplier feeds and product information automatically. If attackers inject malicious content into product metadata or marketplace seller submissions, AI systems may update incorrect prices, trigger unauthorized promotions, or generate misleading product descriptions. Even small pricing errors can create significant financial losses when applied across thousands of products.
RAG and Knowledge Base Poisoning
Retrieval-Augmented Generation (RAG) is a technique that allows AI systems to retrieve information from enterprise knowledge repositories before generating responses.
This can lead to compliance violations, operational disruption, exposure of confidential information, and poor business decisions.
Supply Chain Workflow Manipulation
AI increasingly processes shipment updates, purchase orders, inventory planning data, and vendor invoices across retail supply chains.
A manipulated file entering one of these workflows can influence procurement decisions, stock replenishment priorities, vendor payments, and shipment scheduling without directly attacking infrastructure.
In some cases, manipulated content can affect procurement approvals, stock replenishment decisions, shipment priorities, and vendor payment workflows simultaneously, creating disruption across multiple areas of the business.
The Business Impact Goes Beyond Cybersecurity
Retail operates in an environment where customer trust, operational speed, and profitability are tightly connected.
When AI systems are manipulated, the consequences can spread quickly across multiple business functions.
Potential impacts include:
- Financial fraud
- Unauthorized refunds
- Customer data exposure
- Inventory disruption
- Supply chain delays
- Compliance violations
- Revenue loss
- Reputational damage
- Loss of customer trust
Unlike traditional cyberattacks, these incidents may remain undetected longer because the AI appears to be functioning normally. The system is not broken. It is simply acting on compromised information.
That is why AI risk management must become a business priority rather than a purely technical concern.
Strengthening AI Data Ingestion Security
As cybersecurity trends in the retail industry continue to evolve, organizations must begin treating AI ingestion pipelines as critical security infrastructure.
Organizations should validate external content before it enters AI systems, separate system instructions from external inputs, limit permissions, maintain human oversight for high-impact decisions, secure knowledge repositories, and monitor for unusual AI behavior through AI-powered threat detection capabilities.
Modern AI governance must extend beyond the model itself. Retail enterprises should govern data ingestion processes, embedding pipelines, retrieval systems, AI-generated actions, prompt handling, and audit logging with the same rigor applied to traditional enterprise systems.
At HTC, we believe organizations should secure AI the same way they secure critical business processes. That means combining governance, monitoring, human oversight, and operational controls across the entire AI lifecycle, not simply protecting the model itself.
Strong AI risk management practices are becoming essential for maintaining retail data security, customer data protection, retail data privacy, and broader enterprise cybersecurity resilience.
A Simple Way to Understand the Risk
A useful way to think about AI is as an extremely capable junior employee operating at extraordinary speed but with limited judgment.
It trusts what it reads, follows instructions literally, and often lacks the context needed to recognize manipulation or question intent.
Without proper guardrails, that combination can create significant operational and cybersecurity risks. The more authority organizations grant to AI systems, the more important it becomes to supervise, validate, and govern the information they consume.
How HTC Can Help
As retail enterprises accelerate AI adoption, the challenge is no longer simply deploying intelligent systems. It is ensuring those systems remain secure, governed, and resilient.
HTC helps organizations strengthen AI adoption through AI Security Assessments, AI Governance Frameworks, AI Data Pipeline Security Reviews, and continuous AI Trust and Risk Monitoring. By combining governance, monitoring, human oversight, and operational controls, HTC helps retailers build AI ecosystems that are secure, scalable, compliant, and trusted.
The Path Forward
AI data ingestion is becoming one of the most important cybersecurity challenges facing modern retail enterprises.
As retailers continue integrating AI across customer experiences, operations, and retail supply chains, attackers are increasingly shifting from traditional exploits toward manipulation through language, context, and trusted content.
The organizations that succeed will focus not only on building intelligent AI systems, but also on securing the data, repositories, and workflows that influence AI decisions.
Responsible AI adoption requires more than protecting the model itself. It requires protecting the entire ecosystem surrounding the model.
For retail organizations, securing AI data ingestion today may ultimately determine how safely and successfully AI can scale tomorrow.